
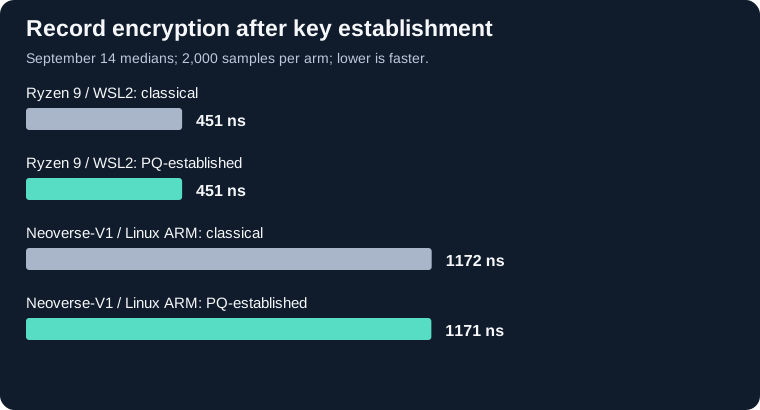
Moving to post-quantum protection does not have to make every encrypted record bigger. In 8DB's controlled record-encryption tests, a 115-byte input produced 131 bytes of ciphertext with either classically established or post-quantum-established keys. The cipher stayed the same, AES-256-GCM-SIV. On the later paired x86 and ARM runs, median encryption times were effectively unchanged at the measured resolution. Paired measurements
The practical benefit is keeping a compact, fast symmetric record path while changing how its key is established. Key setup, signatures, framing and delivery still have costs. This comparison isolates the encrypted record; it is not a claim of zero overhead for a complete protected database.
8DB brings that design into an embeddable, omnimodal engine. Its wider proposition is protected local storage, recipient-protected exchange and a managed path for cryptographic change, qualified for the workload you intend to deploy.
Where this puts 8DB in the market
8DB's case is integrated protection across the data's life. Oracle and Db2 provide PQ connection options; MongoDB can keep encrypted fields unreadable to its server; SQLCipher and Couchbase Lite bring storage to the device. The meaningful comparison is the protected application each approach delivers, including what your team must assemble.
| Product or stack | Documented starting point | Buyer question that distinguishes the approaches |
|---|---|---|
| 8DB | Protected local storage, authenticated PQ recipient exchange and tested migration/recovery paths | Does its supported integrated profile fit your records, endpoints and recovery requirements? |
| Oracle Database | PQ TLS key exchange and signatures with the specified provider; encrypted server storage | Where does TLS terminate, and which intermediaries need access to plaintext? |
| IBM Db2 | Quantum-safe connection capabilities in the documented release | How will server connection protection join your endpoint storage and sharing workflow? |
| PostgreSQL + OpenSSL | Configurable TLS groups; PQ negotiation depends on the libraries and clients | What must you add for protected local storage and recipient-encrypted messages? |
| MongoDB CSFLE | Application-side field encryption before data reaches the server | Do its field and query semantics fit the job, and what provides the device-local store? |
| SQLCipher | Encrypted embedded SQLite storage and migration tools | What supplies identity, recipient exchange and the wider recovery procedure? |
| Couchbase Lite | Embedded storage, encrypted databases and resilient peer synchronization | How do the required PQ profile, relay trust and supported queries compare? |
A capability comparison, not a performance league table. Sources: Oracle, IBM, PostgreSQL, MongoDB, SQLCipher, Couchbase Lite storage and peer synchronization.
The buying question is how much of your protected workflow comes together inside the engine. Evaluate useful data access, key establishment, integrity and recovery as one application responsibility.
Keep the fast record path
115-byte input · AES-256-GCM-SIV · Ciphertext only
Same input. Same encrypted-record size.
Common scale within this figure: 0–150 B. Smaller is more compact.
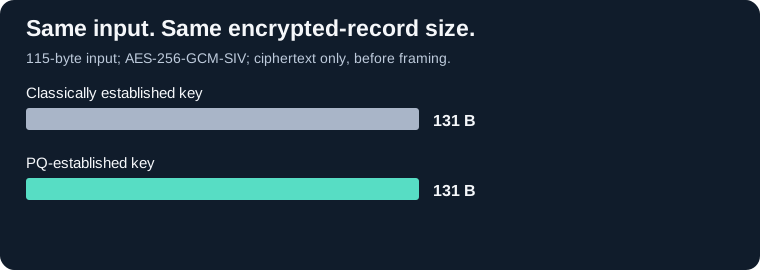
The later paired measurements used 2,000 samples per arm, after 16 warm-ups. The x86 system recorded 451 ns for both encryption medians. The ARM system recorded 1,172 ns and 1,171 ns; that one-nanosecond difference is below the observed 33 ns clock increment. These are measurements of the same cipher after key establishment, not durable write latency.
September 14 medians · 2,000 samples per arm after 16 warm-ups
Keep the fast symmetric record path.
Common scale within this figure: 0–1,300 ns. Lower is faster; compare paired arms within each host.
The economics become clearer when the boundaries stay visible. Large asymmetric objects belong at their actual key, message or integrity boundary. The measured record adds the same 16-byte authentication tag in both arms. The node-message path separately establishes and authenticates each frame; its costs must be included when benchmarking delivery.
Choosing a different protection profile changes the work. A separate provider test returned 185 bytes for a committed AES-GCM profile versus 136 bytes for the framed research-SIV profile. The extra 49 bytes carry a frame byte and key-commitment tag. This is the cost of a different protection contract, not a contradiction of the same-cipher result. Profile measurements
Protect the next cryptographic change, too
Stored information can outlive its original cryptographic configuration. A useful migration must preserve records and indexes, recover interrupted work and satisfy the application's service requirements.
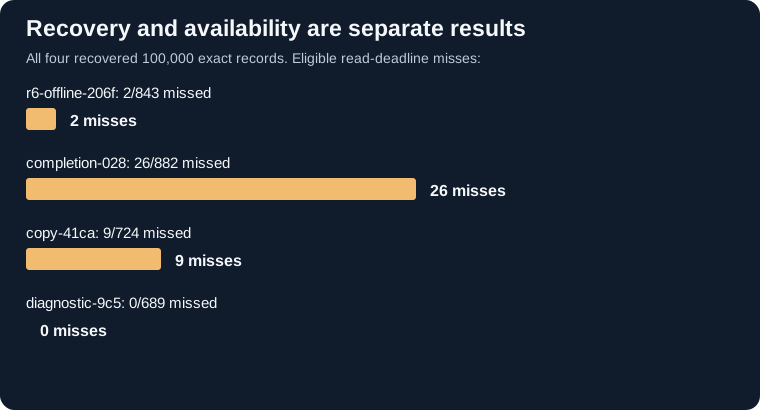
Across four 100,000-record migration runs, 8DB cold-reopened and verified every authenticated, indexed, exact typed record with zero cold-validation errors. The workload changed key derivation from HKDF-SHA-256 to HKDF-SHA-384 while retaining AES-256-GCM-SIV. It included a process kill, cold resume, concurrent reads and record changes. Migration evidence
All four runs recovered every record. Availability is the next dimension to qualify against the application’s service target; the evidence retains the read-deadline results for each run.
Each cold-reopened and verified 100,000 records · Read availability measured separately
Exact recovery in all four runs.
Common scale within this figure: 0–30 misses. Fewer missed deadlines is better; denominators differ.
Put protection beside useful data
An application may need a record, its relationships, a time series and a similarity search. 8DB brings those native modalities into a common engine, creating a foundation for useful data and protection to work together. Start an evaluation with the combination your application needs.
See our separately measured key-value, graph, analytics and time-series results. They show other native capabilities, rather than the performance of one combined protected workload.
Bring one dataset, the endpoints allowed to read it and the interruption it must survive. Plan an 8DB evaluation around protection, useful queries and the complete cost.
Evidence scope Paired record-encryption measurements · Migration and recovery separately measured · Public source records. Explore the evidence. The reviewed integrated profile uses a defined structured-record schema; integrating and qualifying your schema is the first step of an evaluation. Methods and retained scope notes.
Continue the technical conversation
Where could this help your work?
Bring a research question, a database workload or an application you want to build. Let’s connect the ideas in this article to an evaluation that matters to your team.
Discuss this work